Views:162Views
Type:Other
Date:2026-05-07?
Description:The IPSec VPN security gateway series of products have officially passed the rigorous testing and expert review conducted by the Commercial Cryptography Testing and Certification Center of the Natio……
Telephone:010-61460001
The IPSec VPN security gateway series of products have officially passed the rigorous testing and expert review conducted by the Commercial Cryptography Testing and Certification Center of the National Cryptography Administration, successfully obtaining the National Commercial Cryptography Product Certification. Currently, multiple units have conducted trials and received positive feedback and high recognition. The products not only support comprehensive encryption of data transmission, strong identity authentication, and integrity protection, but also effectively resist security threats such as network eavesdropping, data tampering, and identity impersonation, providing a solid underlying support for users to build a secure, trusted, and controllable network environment.
Product Introduction
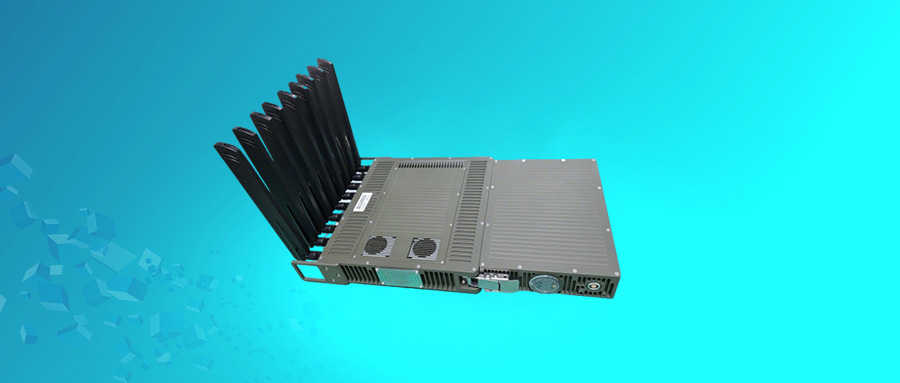
The IPSec VPN security gateway series products are high-performance cryptographic security devices independently developed by Lianshan Technology. They comply with the requirements of GM/T 0023 “IPSec VPN Gateway Product Specification” and GM/T 0028 “Cryptographic Module Security Technical Requirements” Level 2 issued by the National Cryptography Administration. These products have passed the testing and appraisal conducted by the National Cryptography Administration and obtained the commercial cryptographic product model certificate, making them security gateway products with completely independent intellectual property rights. The products mainly include the following functions: multi-link fusion optimization, trusted identity authentication, encrypted transmission, role authorization, IPSecVPN, etc., as well as basic access control functions. They are independently controllable, powerful in performance, scalable, and easy to manage.
The gateway is equipped with a high-speed cryptographic chip approved by the National Cryptography Administration, fully supporting SM2, SM3, and SM4 cryptographic algorithms, meeting the IPSec design standards, and providing users with secure and efficient cryptographic application services. Through flexible deployment, it can fulfill various network interconnection needs such as remote access between headquarters and various branches, partners, and mobile office personnel, while providing security protection measures such as confidentiality, authenticity, and integrity for data transmitted in these remote networks.
Organizational application:

Remote office encrypted access
(1) User requirements
With the rapid development of electronic, informational, and terminal intelligent government systems, remote business trips and office work have become the norm. While meeting users’ remote office needs, it is essential to ensure that personnel can safely access the organization’s internal network to handle daily work when they are away, while also ensuring the legitimacy of the accessing user’s identity and the security of data.
(2) Solution
This solution deploys a wireless security gateway at the front end of the organizational intranet service system, providing a “two-factor” authentication mechanism based on smart password key M2 digital certificate and login password for remote mobile office users, ensuring the legitimacy of the login user’s identity.
Users log in to the security gateway for identity authentication and session negotiation through the digital certificate stored in the smart password key KEY. After the negotiation is successful, an IPSec tunnel is established between the user and the security gateway to enable encrypted transmission of interactive data and authorized access.

Wireless HD video transmission (1) User demands: The rapid development of mobile internet infrastructure has led to increasingly frequent video transmission based on the Internet, with more and more important real-time video data being transmitted over the network, and higher and higher security requirements. Given the one-way audio and video transmission nature of video surveillance, a secure method is needed to ensure secure access to data while achieving audio and video transmission.
(2) Solution: This solution establishes a transmission channel for video transmission at the network and communication security levels, utilizing 4G/5G networks and IPSeCVPN security gateways that support the IPSec protocol and the national cryptographic algorithms SM2, ISM3, and ISM4. By deploying wireless security gateways at both the IP video source and the user end, it helps users achieve security in video transmission. The unique Site-to-site security mechanism of IPSec can maximize the confidentiality, integrity, and non-repudiation of identity between devices.

Remote equipment maintenance collaboration (1) User demands With the increasing demand for remote equipment support and remote video maintenance, user organizations require an efficient, flexible, and secure audio and video conferencing solution to support collaborative work and cross-regional communication in remote maintenance. Such a solution should not only meet the needs of enterprise information management and confidentiality, but also be compatible with different conference terminals and support customized requirements for specific network protocols.
(2) Solution: This solution establishes an independent, secure, and private video conferencing environment by deploying a security gateway and video conferencing server at the intranet boundary of the headquarters (center), without relying on external cloud services. This deployment approach enables enterprises to independently control the storage and transmission process of conference data, effectively avoiding the risk of information leakage and ensuring the security of sensitive information. Additionally, it supports multiple terminal devices, including computers, mobile phones, tablets, VR glasses, etc. Users can choose the appropriate device according to their actual needs, achieving convenience and flexibility in participating in meetings anytime and anywhere.

Interconnection and Encryption between Headquarters and Branches (1) User Requirements: For organizations such as government agencies, political parties, military, and enterprises with multiple branches across different regions, they possess the attributes of geographically dispersed access and centralized deployment of information and data. A secure method is needed to achieve interconnection and interoperability between networks in different regions while ensuring secure access to data.
(2) Solution: This solution provides security gateway products that meet the requirements of cryptographic evaluation and Class 3 of the Cybersecurity Level Protection 2.0 standard for the network and communication security of data systems accessed by various institutions. It integrates multiple operator networks for converged networking and employs IPSec VPN security gateways that support the IPSec protocol and the national cryptographic algorithms SM2, SM3, and SM4. By deploying security gateways at the intranet boundaries of headquarters (centers) and various branches, it helps users achieve secure and high-speed interconnection among multiple branch networks. The unique Site-to-site security mechanism of IPSec can maximize the confidentiality, integrity, and non-repudiation of identity between devices for business interconnection data.

 中文